
Computer scientists have devised an attack that reliably extracts secret cryptographic keys by capturing the high-pitched sounds coming from a computer while it displays an encrypted message.
The technique, outlined in a research paper published Wednesday, has already been shown to successfully recover a 4096-bit RSA key used to decrypt e-mails by GNU Privacy Guard, a popular open source implementation of the OpenPGP standard. Publication of the new attack was coordinated with the release of a GnuPG update rated as "important" that contains countermeasures for preventing the attack. But the scientists warned that a variety of other applications are also susceptible to the same acoustic cryptanalysis attack. In many cases, the sound leaking the keys can be captured by a standard smartphone positioned close to a targeted computer as it decrypts an e-mail known to the attackers.
"We devise and demonstrate a key extraction attack that can reveal 4096-bit RSA secret keys when used by GnuPG running on a laptop computer within an hour by analyzing the sound generated by the computer during decryption of chosen ciphertexts," the researchers wrote. "We demonstrate the attack on various targets and by various methods, including the internal microphone of a plain mobile phone placed next to the computer and using a sensitive microphone from a distance of four meters [a little more than 13 feet]."
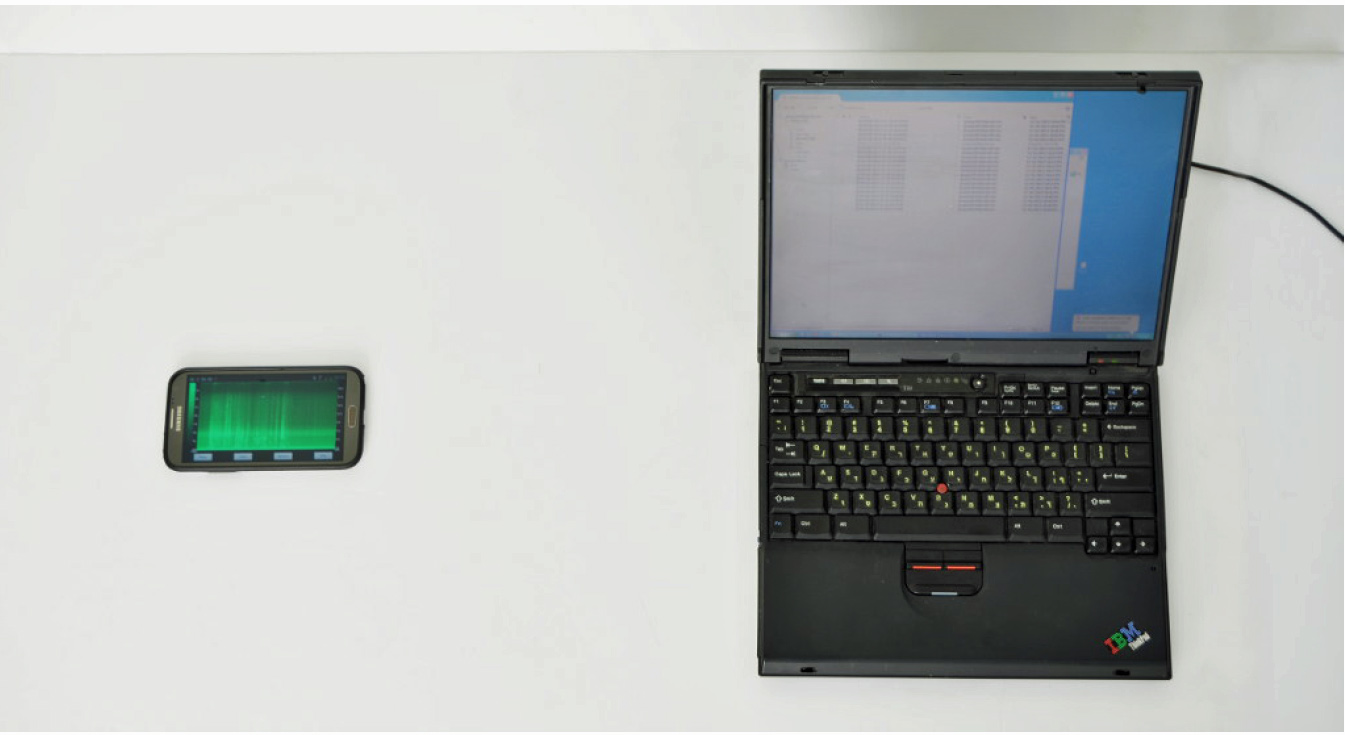
To be sure, the technique has its limitations. Most obviously, the attackers must have a smartphone, bug, or other microphone-enabled device in close proximity to a computer at the precise moment it's decrypting a message that was sent by, or otherwise known to, the attackers. Still, the technique represents a solid advance in the field of cryptanalytic side-channel attacks, which target cryptographic implementations that leak secret information through power consumption, electromagnetic emanations, timing differences, or other indirect channels.
It's certainly feasible to know the contents of an encrypted message on a target's computer as long as the attacker knows the target's public key and succeeds in getting the target to decrypt the message. What's more, the researchers proposed several techniques and scenarios that could help attackers overcome the limitations of the acoustic cryptanalysis technique. One is to develop a smartphone app that automates the process of capturing and processing the acoustic emanations coming from the targeted computer.
"An attacker would install this software, reach physical proximity to the target computer under some pretext, and place the phone appropriately for the duration of the attack," the researchers wrote. "For example, in a meeting, the attacker could innocuously place his phone on the desk next to the target laptop and obtain the key by meeting's end. Similar observations apply to other mobile devices with built-in microphones, such as tablets and laptops."
The researchers proposed other attack scenarios, including infecting a target's smartphone with sound-monitoring malware; placing a bug or infected computer or mobile device in a charging station, presentation podium, or other location where PCs are often placed; or keeping a listening device in a server room.
Beyond acoustics, the researchers also demonstrated a similar, low-bandwidth attack that can be performed by measuring the electric potential of a computer chassis. Attackers need only touch the target computer with their bare hand or get the required leakage information from the ground wires at the remote end of VGA, USB, or Ethernet cables. Wednesday's paper, titled "RSA Key Extraction via Low-Bandwidth Acoustic Cryptanalysis," was written by Daniel Genkin and Eran Tromer of Tel Aviv University and Adi Shamir, the cryptographer who is the "S" in RSA and is currently with the Weizmann Institute of Science. The paper comes a few weeks after separate researchers devised a technique that infected computers could implement to jump air-gaps used to isolate sensitive machines from the Internet.
The attack works by monitoring sounds emanating from the CPU of a targeted computer. By focusing on sounds commonly made when many computers ran GnuPG the scientists found they could distinguish between the acoustic signature of different RSA secret keys (signing or decryption) and fully extract decryption keys by measuring the sound the machine makes during decryption of chosen ciphertexts.
"The acoustic signal of interest is generated by vibration of electronic components (capacitors and coils) in the voltage regulation circuit, as it struggles to maintain a constant voltage to the CPU despite the large fluctuations in power consumption caused by different patterns of CPU operations," the researchers wrote in this summary. "The relevant signal is not caused by mechanical components such as the fan or hard disk, nor by the laptop's internal speaker."
The techniques they demonstrated certainly aren't viable for casual attacks. Still, as Wednesday's updates from GnuPG attest, they represent a realistic threat for people who use cryptographic software and devices in certain settings. The researchers outline several countermeasures application developers can implement to prevent computers from leaking the secret keys in acoustic emanations, namely a technique known as RSA ciphertext randomization. People who rely on cryptography applications should check with the developers to make sure they're not susceptible. In the meantime, end users shouldn't assume that running a computer in a noisy environment will prevent attacks from working, since acoustic emanations that leak secret keys can often be filtered.